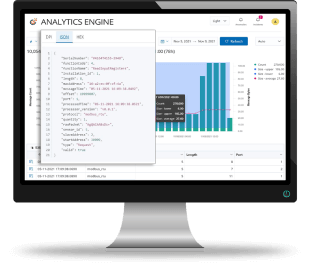
AnalytICS Engine Enables You to Detect Cyber-Physical and Operational Incidents on Your Legacy ICS to Increase Asset Uptime and Avoid Asset Damage
AnalytICS Engine operates as an intrusion detection system (IDS), enabling you to securely capture, baseline, analyze trends and create alerts on serial communications network behavior. The analytical platform streamlines the security analysis process by gathering encrypted serial data packages sent by SerialGuard sensors and performs thorough deep packet inspections to formulate metrics and visualizations of the assembled data. The platform can be deployed on-premise or as a service, providing you with an easy-to-use set of intuitive tools to monitor communications.
The AnalytICS Engine:
- Flags anomalous communications to detect cyber and operational incidents in your ICS
- Performs deep packet inspection and derives summary metrics for serial communication
- Remotely manages your SerialGuard sensors
- Integrates with SIEMs to support your pre-existing security workflows
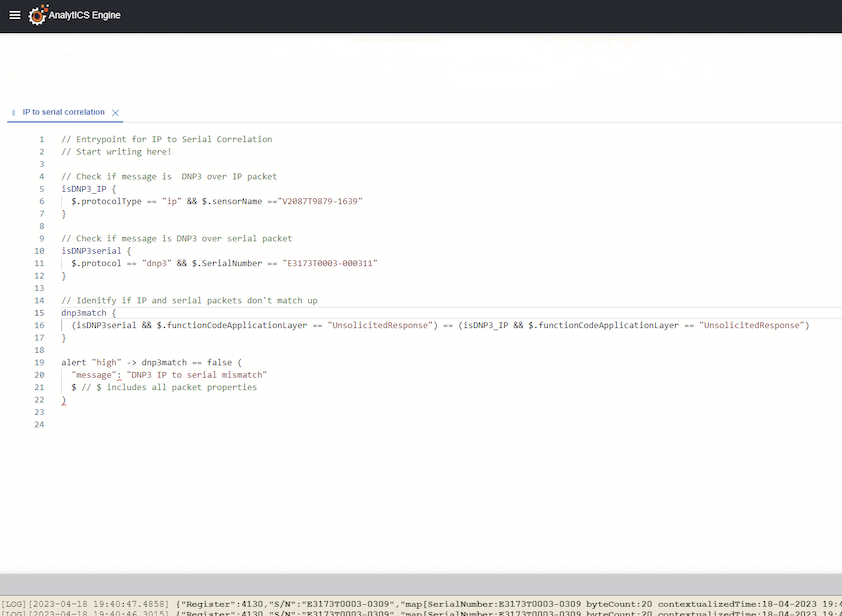
CyRenQL™ – The Cynalytica Query Language
The Evolutionary High Performance Integrated Query Programming Tool for IP and non-IP ICS/SCADA in OT Environments
Cynalytica Query Language (CyRenQL):
- Provides users the ability to create cross network alerts, integrations, and other triggers from the AnalytICS Engine
- Delivers NOC/SOC operators and analysts a platform that can simultaneously query and correlate data across analog, serial, and TCP/IP ICS/SCADA communications
- Provides operations centers improved visibility, comprehensive threat detection, faster incident response, enhanced situational awareness, and greater efficiency
- Enables tailored machine learning and AI by providing a unified platform to access, analyze, and integrate data from disparate sources
The Cynalytica AnalytICS Platform in Action
Detecting Malicious Data & Advanced Attacks
(False Feedback Attacks & Other Malicious Data)
Serial Communications Asset & Configuration Change Management
Troubleshooting and Diagnostics
Nozomi Networks & Cynalytica Solutions Brief